
honestly at this point I don’t consider it worth continuing the discussion here, as it doesn’t seem that you understand enough of what you’re talking about, despite your claims of dealing with it for “years”, yet you keep implying that i’m likely the one being wrong or even lying/misrepresenting things.
the second screenshot is from the same browser as the first, both are in firefox, using the tor browser variant in safest mode, which blocks even more than the average noscript installation in firefox. tor browser is a hardened variant of firefox esr. if it works in tor browser without loading js from third parties it’ll very much do so in any other browser. the screenshot is from macos, which is probably why you’re not used to it, but that’s just what firefox on macos looks like. this is my standard firefox install: 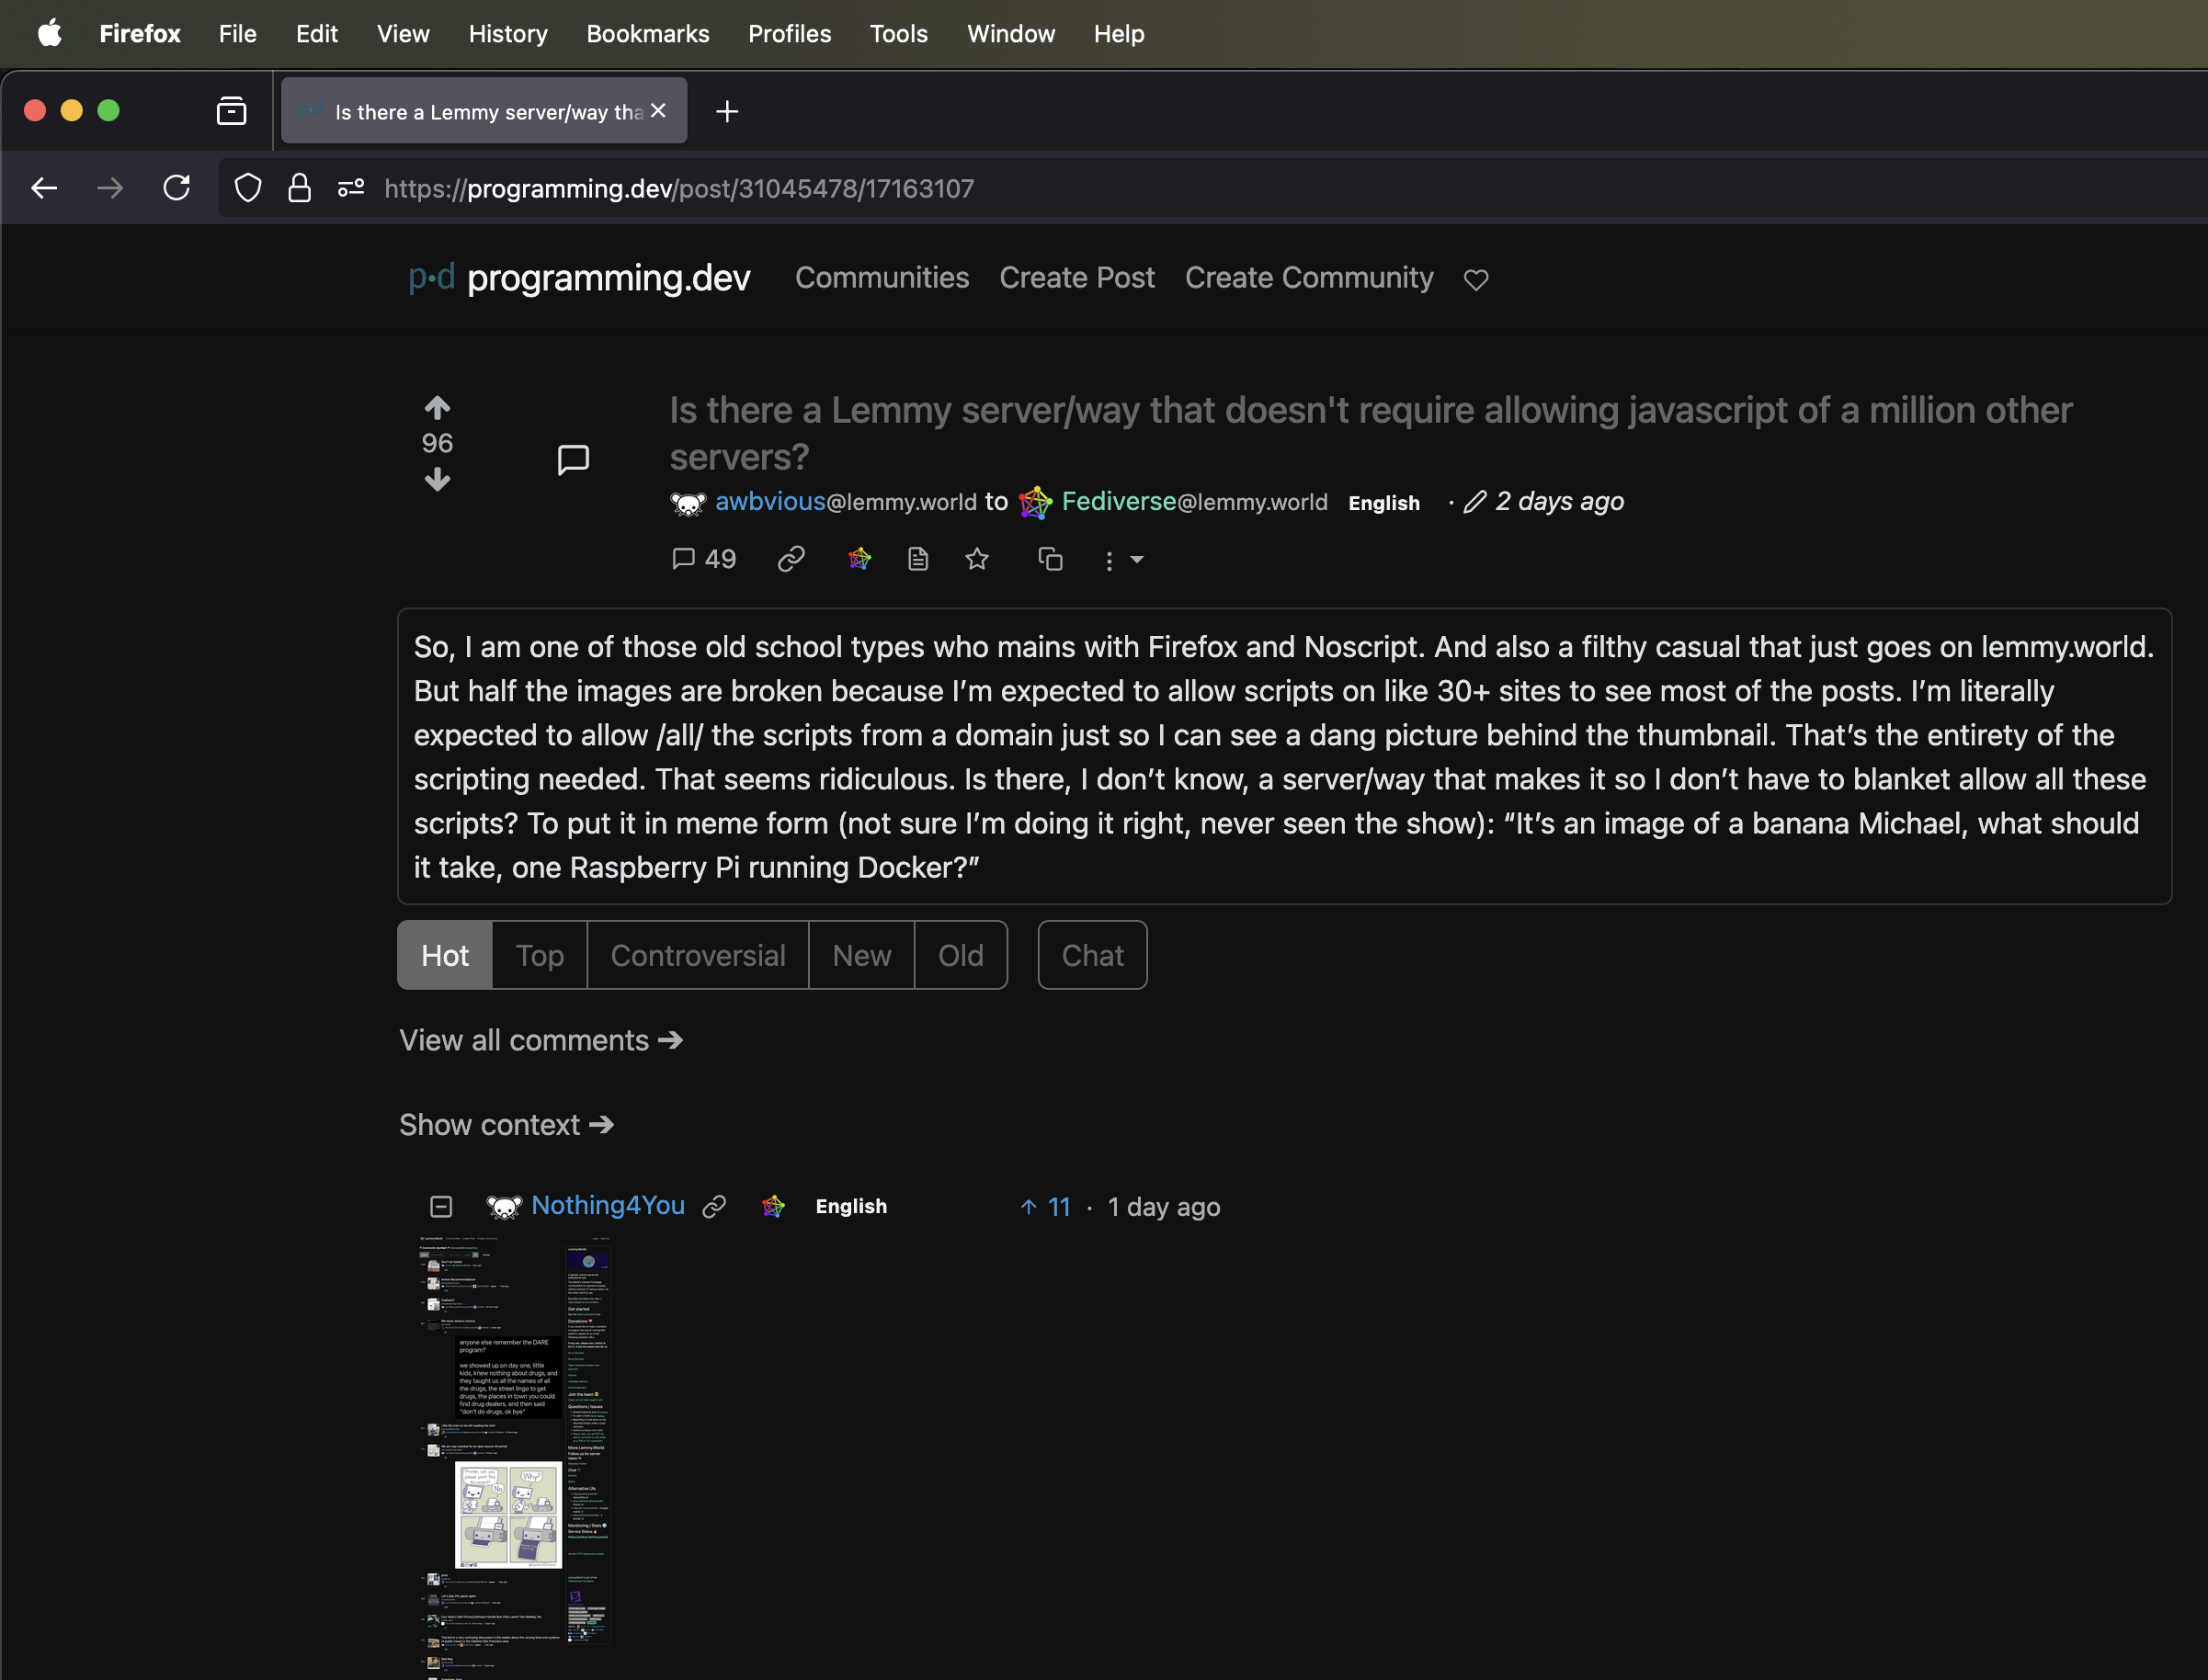
besides, if lemmy was loading and executing javascript from other instances, this would be a massive security issue, which is yet another reason why your claim of loading js from other instances is ludicrous for someone who knows how these things work, at least when you keep insisting on it.
as i mentioned before, noscript is not an extension that is easy to use without some basic understanding of how websites work. if you’ve been having issues for years due to not understanding these things and how to deal with them properly that suggests that it’d probably be better for you to just switch to something like ublock origin with anti-tracking filter lists if you’re not planning to spend some time learning how websites work and what the different types of blocked resources do.
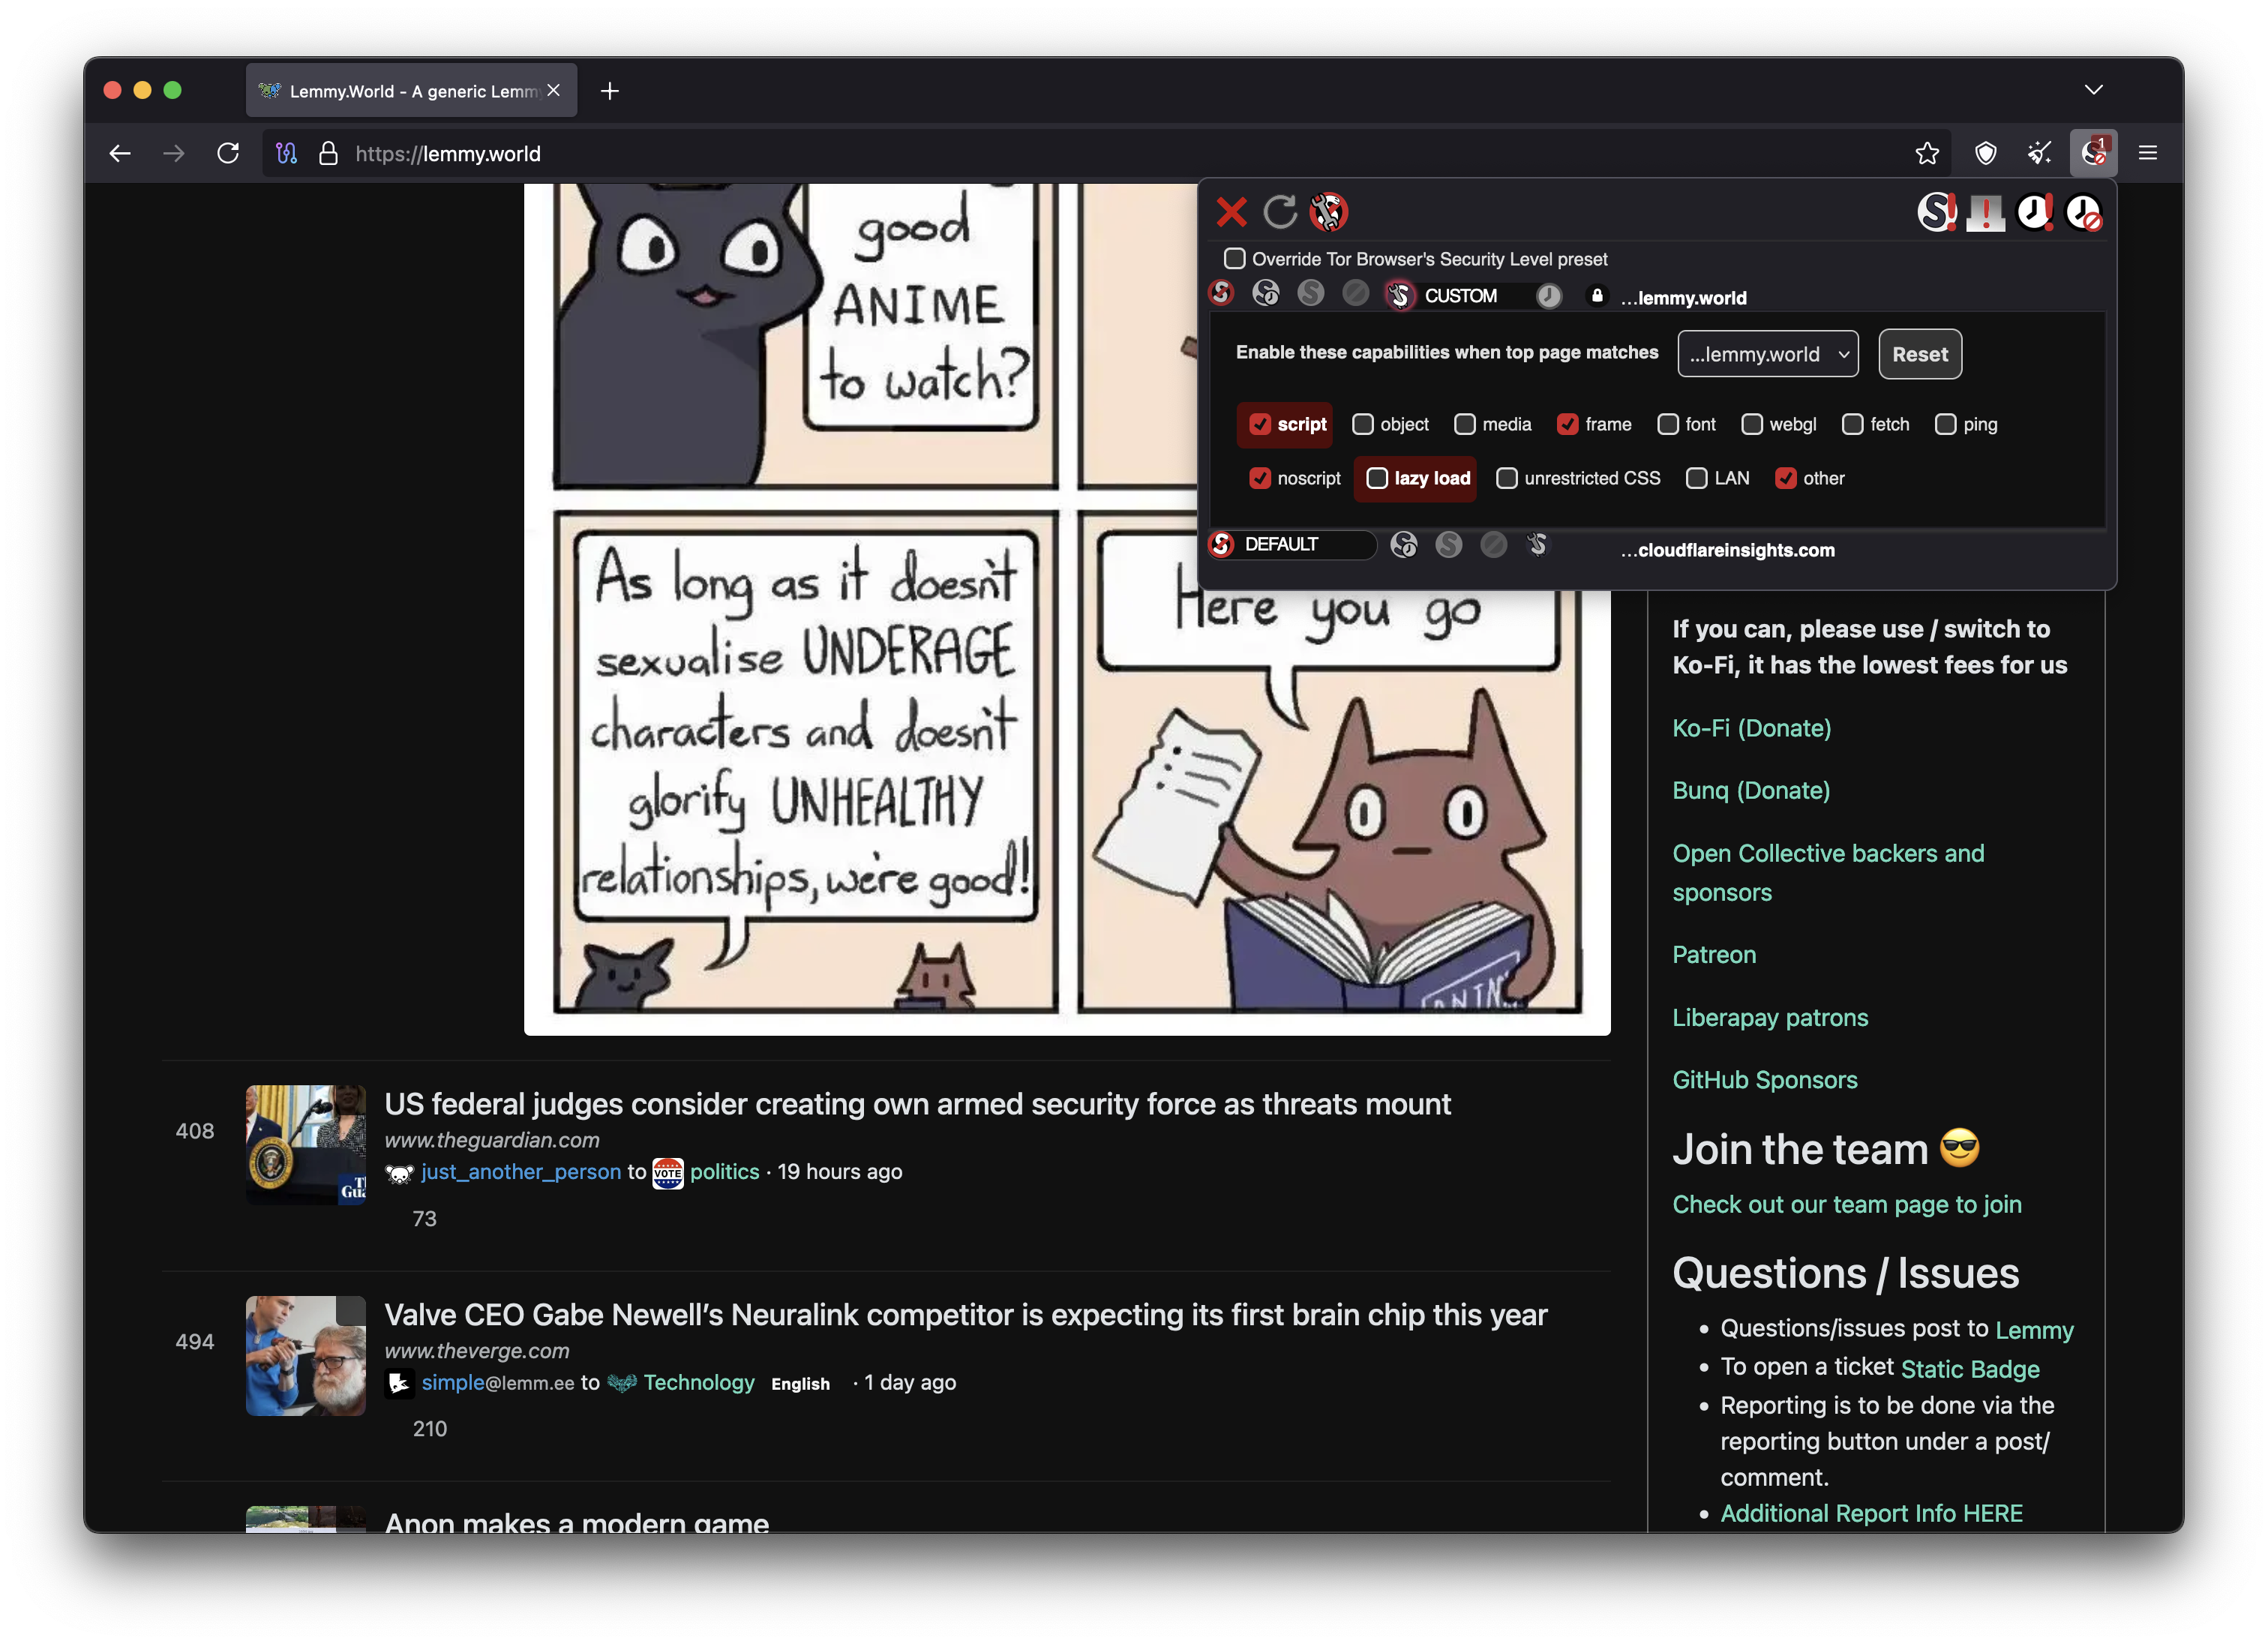
i don’t even see how you would be blocking images with noscript, as there doesn’t even seem to be an option for it. unless of course you’re confusing noscript with something like umatrix, which does allow blocking images by default as well, but it would also clearly show that there is media blocked and not scripts: 
anyway, if you’re truly interested in understanding these things and not just rant about them please do some research on the technology being used.

this is generally something you should avoid doing with activitypub software, as there is no clearly defined way to deal with changed private keys and it is handled differently depending on the software. with lemmy it should more or less resolve itself after some time, as instances will refresh public keys from time to time. after a few days of being alive again and having activities federate out it that part should start working properly again.
check if your instance is considered dead, it may take sending some activities (e.g. subscribing, posting, commenting) and a bit of waiting to get your instance considered reachable again. you can use https://phiresky.github.io/lemmy-federation-state/site to check the instance you’re expecting data from and look for where your instance is listed.
as @asudox@lemmy.asudox.dev already mentioned, all you did was disappear. how would anyone know that your intention was to delete data?
while you can’t force other instances to respect your deletion requests, it would still be possible to ask them for it, but this is not an easy task once they’re no longer in your database. the most effective/efficient way to do this would probably to first get your overall federation fixed/not considered dead anymore, then delete the account using the same name, and never use the username again on the same domain in the future, as deletions are more pretty much irreversible and depending on the software on the other side may permanently block the username from being used, even if you change this in your database. another option could be creating posts/comments with matching ids in the database and then deleting them via api, but this is also rather fiddly and a lot easier to fuck things up with. i don’t recommend editing the db directly without good understanding of lemmy’s internals.
Lemmy uses numeric incremental ids for posts and comments, so when you started with a fresh database these ids are getting reused. this will break your posts and comments from properly federating to instances that have seen them with the same id before.
the easiest and lowest tech solution to deal with this would be to simply move to a different domain/subdomain for a proper new instance experience. alternatively you could consider adjusting the sequences in the database used for new post, comment and pm ids, to ensure that they are higher than any number your instance may have previously seen. as they are incremented not only by local content, but also by content retrieved via federation, these numbers will be significantly higher than the amount of content you had posted in the past, but it will be hit or miss whether they will overlap with ids that were for old local content.
based on counts from lemmy.ml and lemmy.world, it seems that a post sequence starting at 55m is likely safe to use, 20m for comments. pm ids are not publicly visible, but unless you sent or received many in the past, something like 1k or 10k are probably still safe bets. this is a db modification that you will need for sure if you want to minimize federation issues while using the same domain.
looking at your instance i’m not sure if this is what you mean by replies resurfacing, as i don’t see any replies by remote users on your comments, but what i described is otherwise going to cause issues randomly in the future if you happen to hit a previously locally used id on a new local post/comment.